When an Undercover Google Analyst Infiltrated the Ultimate Supply-Chain Hacking Gang
A deep-dive into how Google planted a mole inside TeamPCP, the brazen crew that infected hundreds of open-source packages and breached a thousand companies....
Terrifyingly, modern dependency trees are fragile. Everyone in this industry knows it, yet we routinely pretend our software supply-chain security is rock-solid until some catastrophic event forces us to wake up and look at the actual wreckage. Take TeamPCP. In a remarkably short span, this crew managed to taint hundreds of legitimate open-source repositories, hijack developer credentials, and even deploy a Dune-themed self-spreading worm to automate their pillaging across more than a thousand corporate networks while nobody noticed a single thing.
Though that part is certainly terrifying enough, what makes this particular saga genuinely wild isn't just the sheer scale of the devastation. It While the group was running roughshod over open-source registries and partnering with rival cybercrime syndicates! See the pattern? They were being watched from almost day one by folks who actually knew what they were doing. Google's Threat Intelligence Group didn't just observe the carnage from the outside, but an undercover Mandiant analyst had with ease cultivated a persona. Directly, built real trust — and wormed their way into the hackers' inner circle. And wormed their way into the hackers' inner circle.
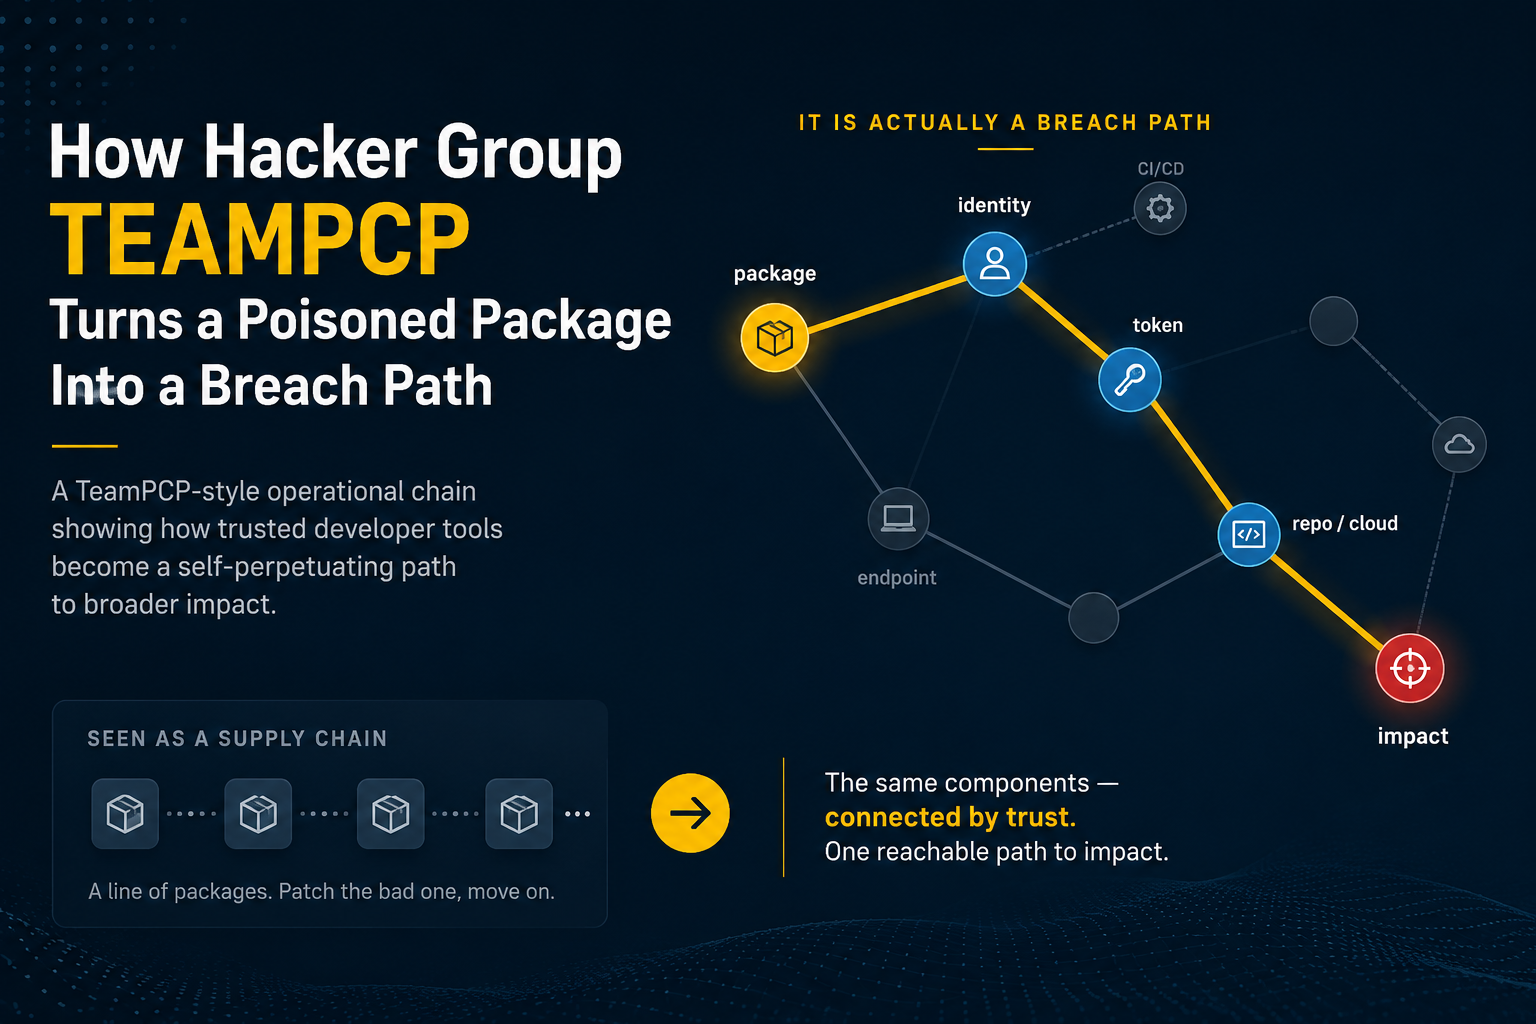
breaking up clever threat actors. Deep social engineering still trumps raw automated telemetry. Truth is, they didn't just wait for slip-ups in daily security – though those inevitably came. Courtesy of youthful ego and remarkably sloppy opsec – because they actually lived inside the machine alongside the masterminds — or so it seems.
Federal police in Australia eventually cuffed two twenty-somethings with help from the FBI. Giving a neat punctuation mark to a terrifying story that reads like a cyberpunk paperback. But why do we still blindly rely on massive webs of third-party libraries maintained by total strangers. Crossing our fingers that nobody malicious has compromised our package managers today? Crossing our fingers that nobody malicious has compromised our package managers today.









