How Kernel-Level Anti-Cheat Became an Industry-Wide Security Nightmare
We handed game developers root access to our operating systems and called it progress. It is time to admit we messed up....
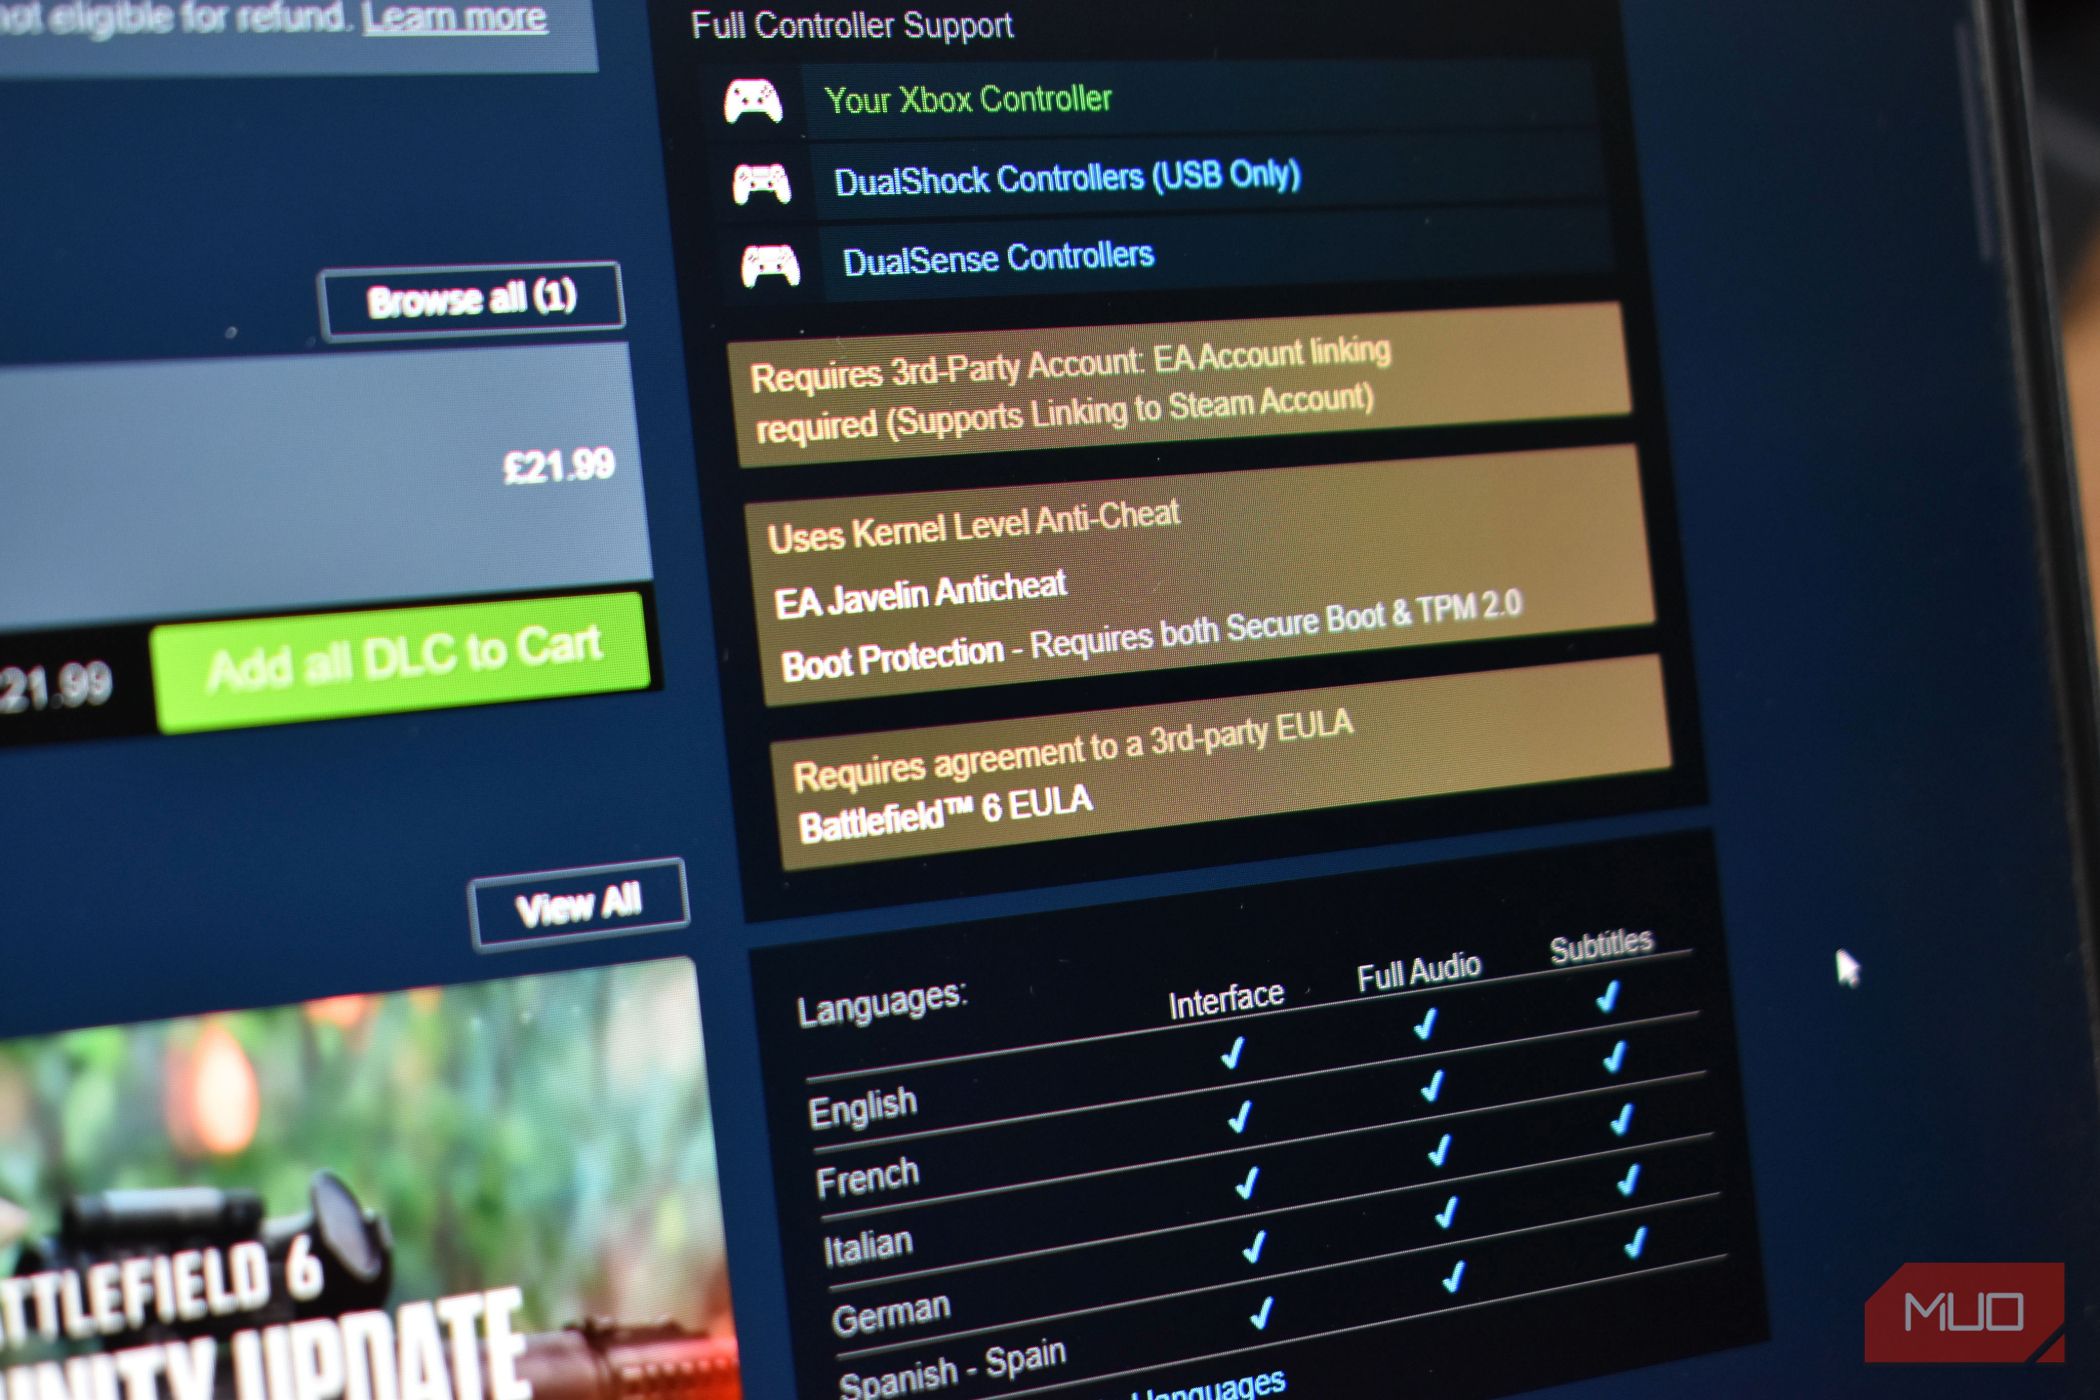
Somewhere along the way, we collectively lost our minds regarding software trust. Handing a video game driver Ring 0 access – the absolute deepest level of your operating system where it can bypass normal security boundaries, read physical memory, and intercept hardware calls – used to sound like malware behavior. Today, it's just the price of admission for a Tuesday night multiplayer match. We have normalized installing what is essentially a commercial rootkit just to play a live-service game, trusting that billion-dollar publishers and their third-party vendors will never experience a catastrophic security lapse, write sloppy driver code, or leave a back door wide open for bad actors to exploit.
The technical reality of kernel-level anti-cheat is horrifying when you actually stop to look past the marketing spin. These drivers load up alongside your operating system during the very start of the boot sequence, lurking invisibly in the background, scanning your RAM, inspecting system hooks, and quietly monitoring everything you do. They have unmitigated hardware and memory access, meaning there is technically nothing stopping a compromised driver from reading your active browser sessions, scraping your password manager, or exfiltrating sensitive local data. And yet, we wave it through because we want to stop teenagers from using aimbots in casual lobbies. It's an absurd trade-off that prioritizes corporate convenience over basic digital hygiene.

History tells us this gamble always ends badly. We've watched real-world incidents where vulnerabilities in these exact kernel drivers – from Easy Anti-Cheat oversights to Hoyoverse's mhyprot2. Sys driver being actively hijacked by ransomware groups to blind antivirus software – turned gaming utilities into direct vectors for system compromise. Bring Your Own Vulnerable Driver attacks thrive on this exact architecture, turning a feature meant to protect fair play into an open invitation for local privilege escalation. When poorly coded kernel code crashes, it doesn't just throw an error message; it takes your entire machine down in a glorious Blue Screen of Death, corrupting boots and frying system stability.
The worst part is that it does not even work. Dedicated cheaters still find workarounds, hardware spoofers bypass detection routines within days, and the only people truly inconvenienced by these draconian measures are Linux enthusiasts and privacy-conscious users who value their system integrity. We need to stop accepting rootkit software as a standard cost of entertainment. Until developers start investing in strong server-side validation and intelligent heuristic detection instead of demanding absolute dominion over our personal hardware, we are walking blindly into a digital security disaster of our own making.









